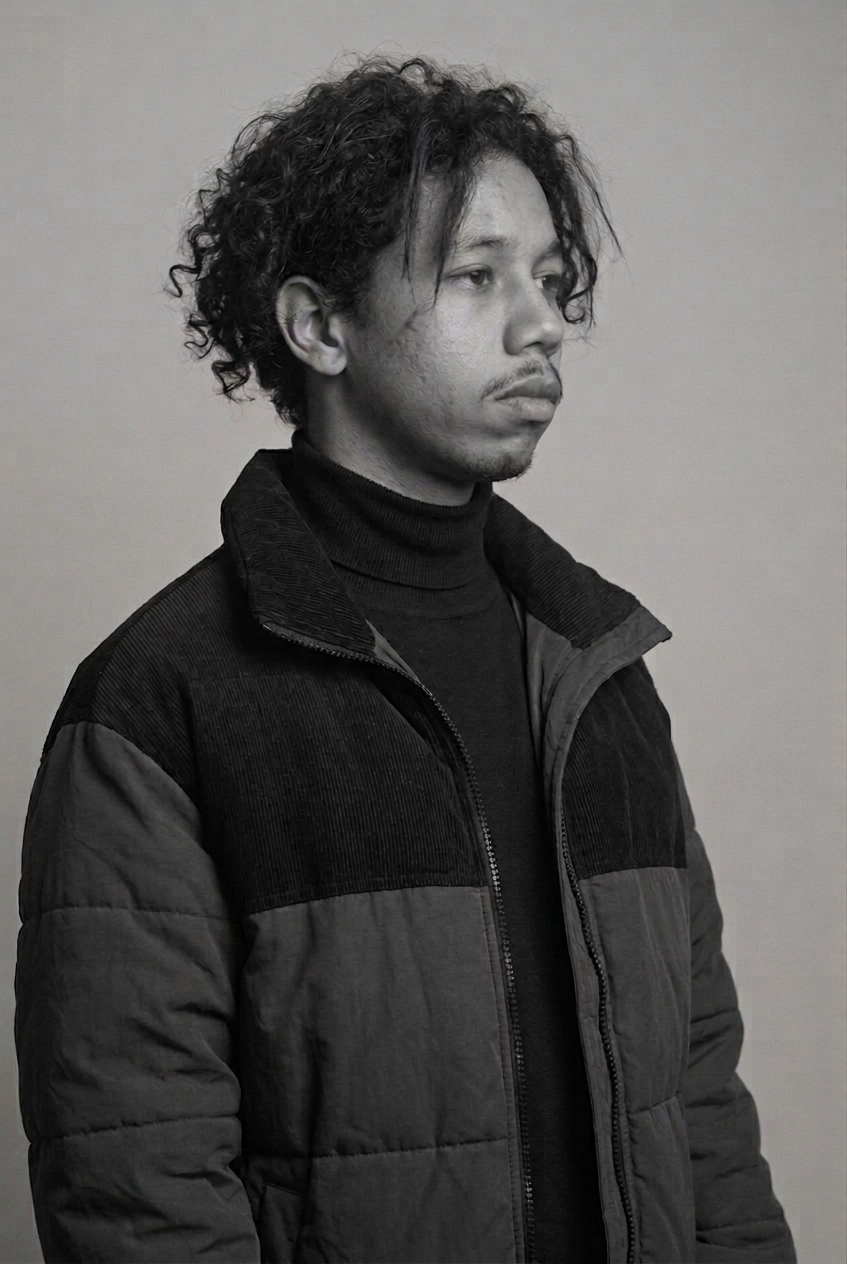
$ whoami
srdusr · Trevor Gray
(noun/alias) • /ˈsərdəzər/
• A combination of the words "sword" and "user", shortened for convenience and styled in the fashion of unix commands.
• Example: srdusr, akin to a command-line ninja, slashes through technical challenges with the agility and precision of a well-honed blade...
I'm a security researcher and software developer based somewhere on the internet. I spend my free time refining my skills, exploring new technologies and always breaking things! When not coding/researching, you can find me optimizing my workflow or practicing modern-day fencing (the one with swords in it).
What I Do
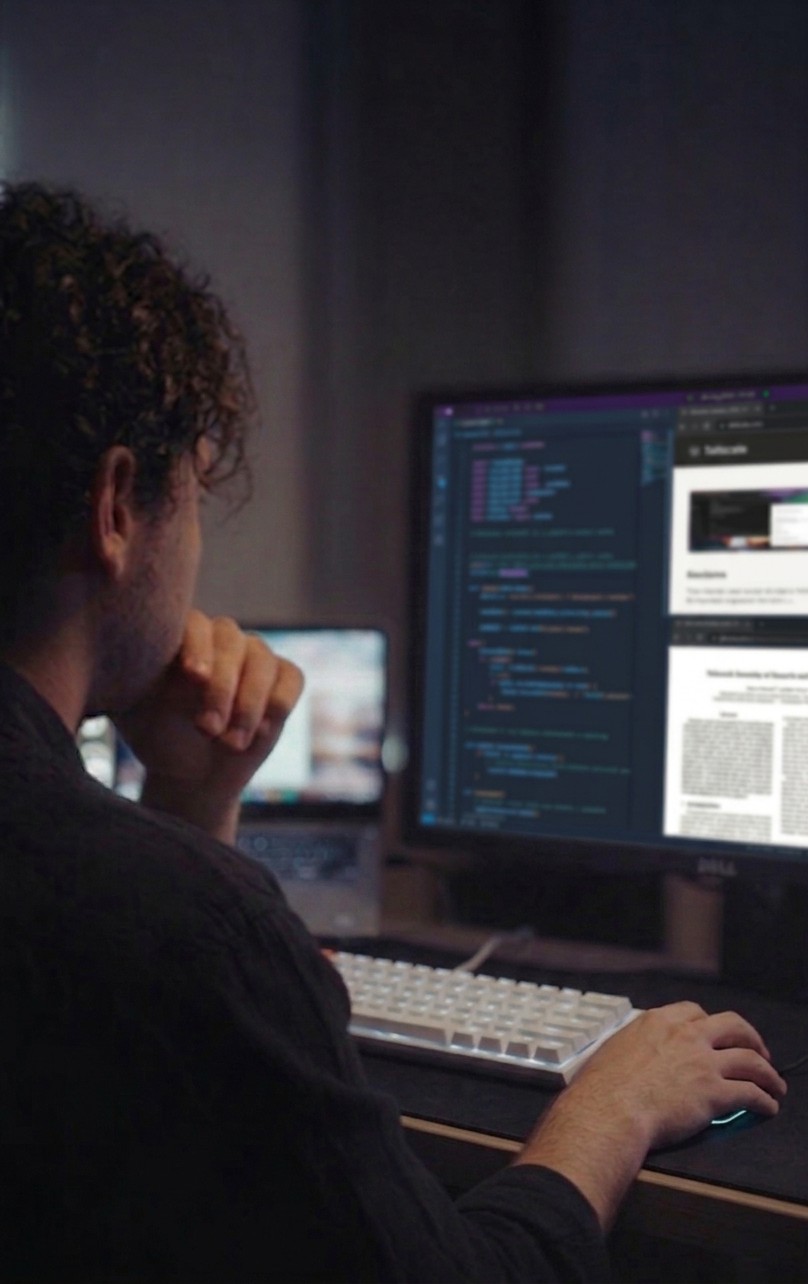
I specialize in offensive security, penetration testing, and vulnerability research. My work involves finding and exploiting weaknesses in systems before the bad guys do, then helping organizations fix them. I build custom tools, automate security workflows, and contribute to open-source security projects.
When I'm not breaking things, I'm building them, from software to infrastructure automation. I believe the best security professionals understand both sides: how to build secure systems and how to break them.
Services
Security testing and the tooling around it, for teams who would rather find the hole themselves first. What that draws on:
Offensive Security
Web & API
Defensive Security
Reverse Engineering
Custom Tooling
Systems & Development
Infrastructure
Networking & Cloud
Automation & Monitoring
Recon & OSINT
Reporting
Current Focus
Most of my time goes into two things right now: attack surface at the kernel and OS level, and building the tooling I keep wishing existed. The commercial tools are good, but they rarely fit the exact shape of a job, so I end up writing my own recon frameworks, fuzzers and analysis tools. The ones that survive contact with real work end up on GitHub.
Alongside that I take on freelance security and infrastructure work, and I run a home lab with SIEM, IDS/IPS and network segmentation. Defending something you built yourself teaches you more about it than any amount of reading.
Get in Touch
Have a system that needs testing, a problem that needs a custom tool built around it, or just want to chat about security research and cool ideas?
Feel free to reach out.